The Platform
Runtime Governance for High-Risk AI Systems
Piscys is developing an independent control layer designed to sit between AI systems and consequential enterprise action. Its proposed architecture brings together verifiable provenance, proportional intervention, accountable authority, and operational evidence — so governance can apply when decisions become consequential.
Built for organizations deploying consequential AI in financial services, healthcare, and other high-accountability workflows.
Advisory Services Available Now — Platform in development.
01 / The Runtime Control Gap
The Gap Between Governance Intent and Action
Enterprise policies can define acceptable AI behavior. Risk assessments can identify where harm may occur. Monitoring can reveal when a system behaves unexpectedly. But none of these measures, on its own, establishes whether a consequential action is authorized at the moment it is attempted.
That requires a governed boundary: clear constraints, proportionate responses, legitimate decision authority, and records sufficient to reconstruct what happened afterward.
The Operational Requirement
Governance Must Reach the Point of Action
Closing this gap requires more than knowing what an AI system did. Organizations need a governed decision boundary that can evaluate consequential actions against defined constraints, determine when intervention is warranted, and establish who has authority to approve, override, or accept residual risk.
Those decisions also need traceable evidence—connecting the action, the applicable controls, the authorized response, and the resulting outcome.
01
Intent
Define policies, constraints and accountable authority
02
Decision
Evaluate consequential action at the point of execution
03
Response
Apply the authorized response and preserve evidence
02 / Proposed Architecture
A Control Layer Designed for Consequential Action
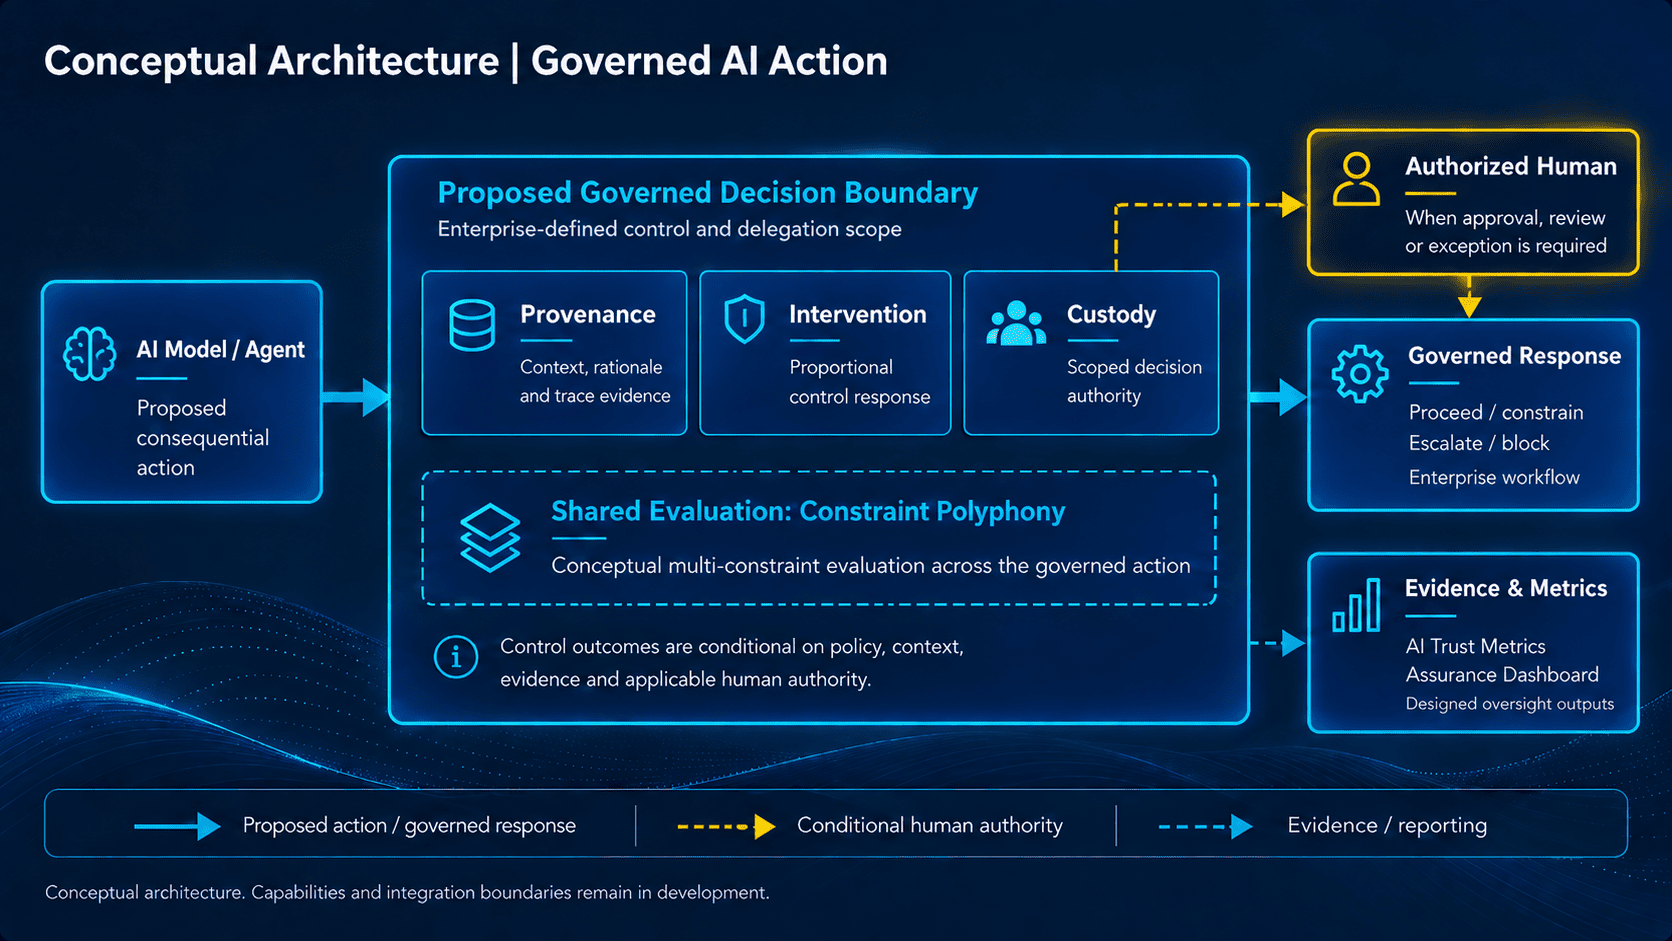
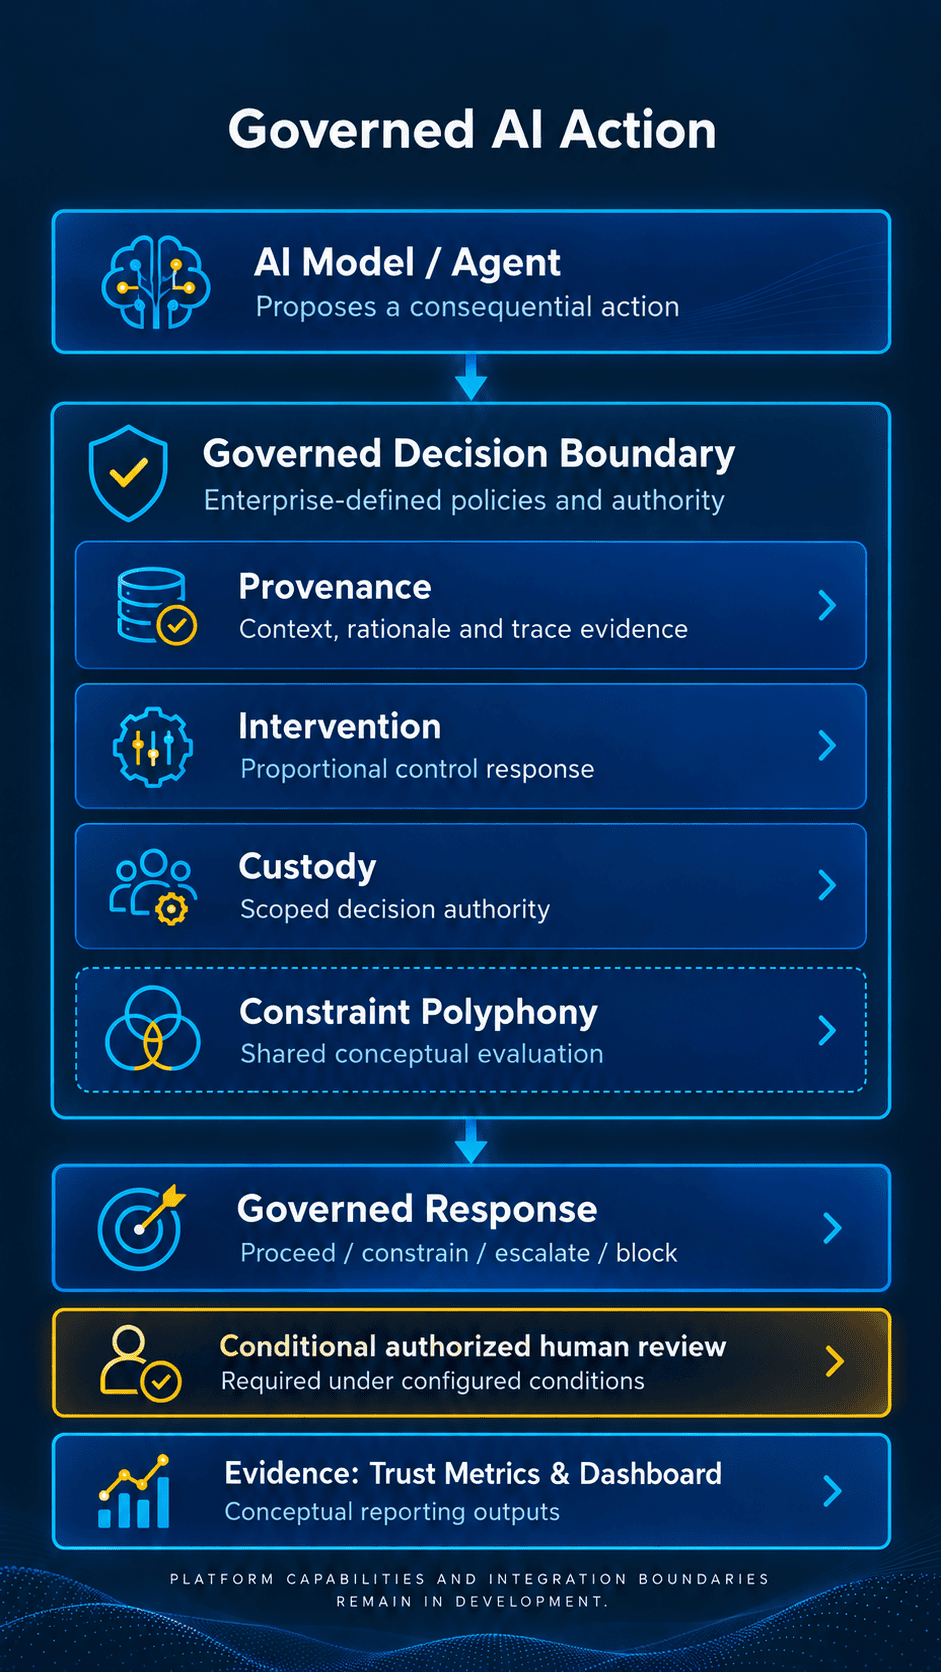
The proposed Piscys architecture places a governed decision boundary between an AI-proposed action and an enterprise workflow. Provenance, Intervention, and Custody are coordinated capabilities — not three mandatory sequential processing stages.
Constraint Polyphony is the shared evaluation approach across that boundary. Authorized human decision-making enters when configured conditions require review, approval, or an exception. AI Trust Metrics and the Assurance Dashboard are intended to make the resulting activity and evidence visible.
03 / Core Engines
Three Coordinated Control Capabilities
The proposed platform combines three coordinated capabilities: Provenance to reconstruct the basis of consequential AI actions, Intervention to apply proportionate controls, and Custody to govern who may set constraints, approve exceptions, and accept residual risk.
01 / Explain
Provenance Engine
Auditable Action Evidence.
Designed to preserve relevant context, constraints, rationale, and event history in cryptographically verifiable records that support reconstruction and
accountable review.
02 / Enforce
Intervention Engine
Proportional Safeguards.
Designed to slow, constrain, escalate, pause, or block proposed AI actions when configured control conditions require a response.
What action was restricted, and what response was warranted
03 / Govern
Custody Engine
Accountable Authority.
Designed to make decision rights explicit: who may establish constraints, authorize exceptions, approve overrides, and accept residual risk — with records of those decisions.
04 / Shared Evaluation
Evaluate the Action From More Than One Angle
Consequential AI decisions may involve competing requirements: evidence sufficiency, operational risk, proportionality, organizational constraints, and legitimate authority. One confident response does not resolve all of them.
Constraint Polyphony is Piscys’ proposed shared evaluation approach for considering interacting governance constraints across the three engines. Where consequential conflicts remain unresolved, the architecture is intended to preserve appropriate human escalation and a traceable decision record.
Read the Constraint Polyphony Research →
This is a high-level architectural concept. Specific polyphony methods, measurements, and decision procedures are not described here.
AUTHORITY IS NOT METADATA
It is part of the
control plane
05 / Operational Assurance
Measure What Governance Actually Changes
AI Trust Metrics are designed to connect runtime control activity to observable outcomes: intervention timing, override patterns, control health, and the completeness of supporting evidence.
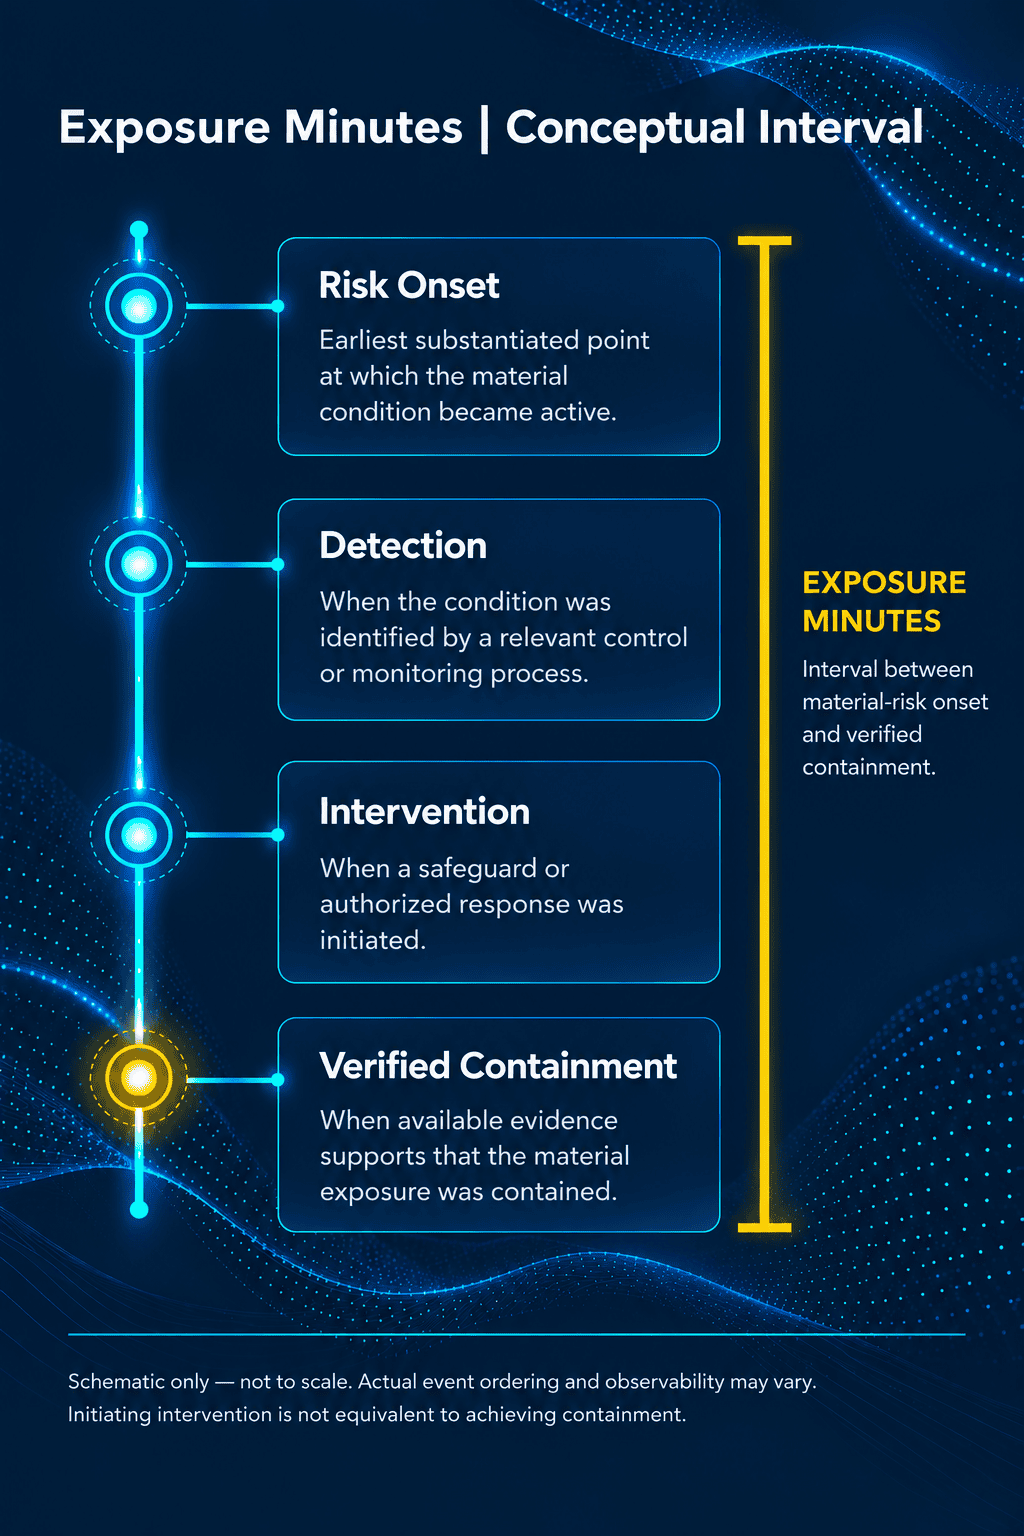
Exposure Minutes is Piscys’ proposed measure of how long a material AI risk condition remains active before verified, accountable containment. The goal is to reduce avoidable exposure over time—not simply count interventions or produce another dashboard.
The proposed Assurance Dashboard would give control teams incident-level visibility, executives and boards qualified aggregate measures, and Piscys a potential means of evaluating customer outcomes as the platform is validated.
01 / Monitor
Control Teams
Examine incident-level exposure, intervention timing, unresolved conditions, and evidence of containment.
02 / Oversee
Executive & Board
Assess aggregate exposure alongside severity, monitoring coverage, incident volume, and control-health trends.
03 / Validate
Customer Outcomes
Evaluate improvement against established baselines and agreed measures of control effectiveness as validation progresses.
Conceptual metrics and dashboard capabilities remain in development. No validated exposure reductions, performance baselines, or service-level commitments are claimed.
06 / Control & Framework Mapping
From Requirements to Control Evidence
Governance requirements become operationally useful when organizations can connect them to defined controls, authorized decisions, and evidence of what occurred.
Illustrative Control Mapping
01 / Define
Requirement
Control Objective
High-risk payment exceptions require documented authorization before release.
02 / Apply
Operational Control
Configured Response
Hold the action, route it to an authorized reviewer, and enforce the approved disposition.
03 / Substantiate
Evidence Record
Reviewable Record
Policy version, trigger, decision authority, response, timestamps, and outcome evidence.
Example: an enterprise-defined control objective for a consequential payment workflow, not a statement that a particular regulation prescribes this exact process.
Framework Reference Points
Framework references are illustrative. Applicability and evidence sufficiency require independent assessment. Piscys does not claim certification or regulatory compliance.
07 / Illustrative Governance Experience
Explore How a Governed AI Workflow Could Work
What might operational AI governance look like when monitoring, intervention, human authority, and verifiable evidence are brought into a shared experience?
Explore Piscys’ proposed governance workflow through an illustrative healthcare scenario—from identifying consequential risk and determining an appropriate response to authorizing decisions and reviewing the resulting evidence.
Select a screen to explore · Click to enlarge
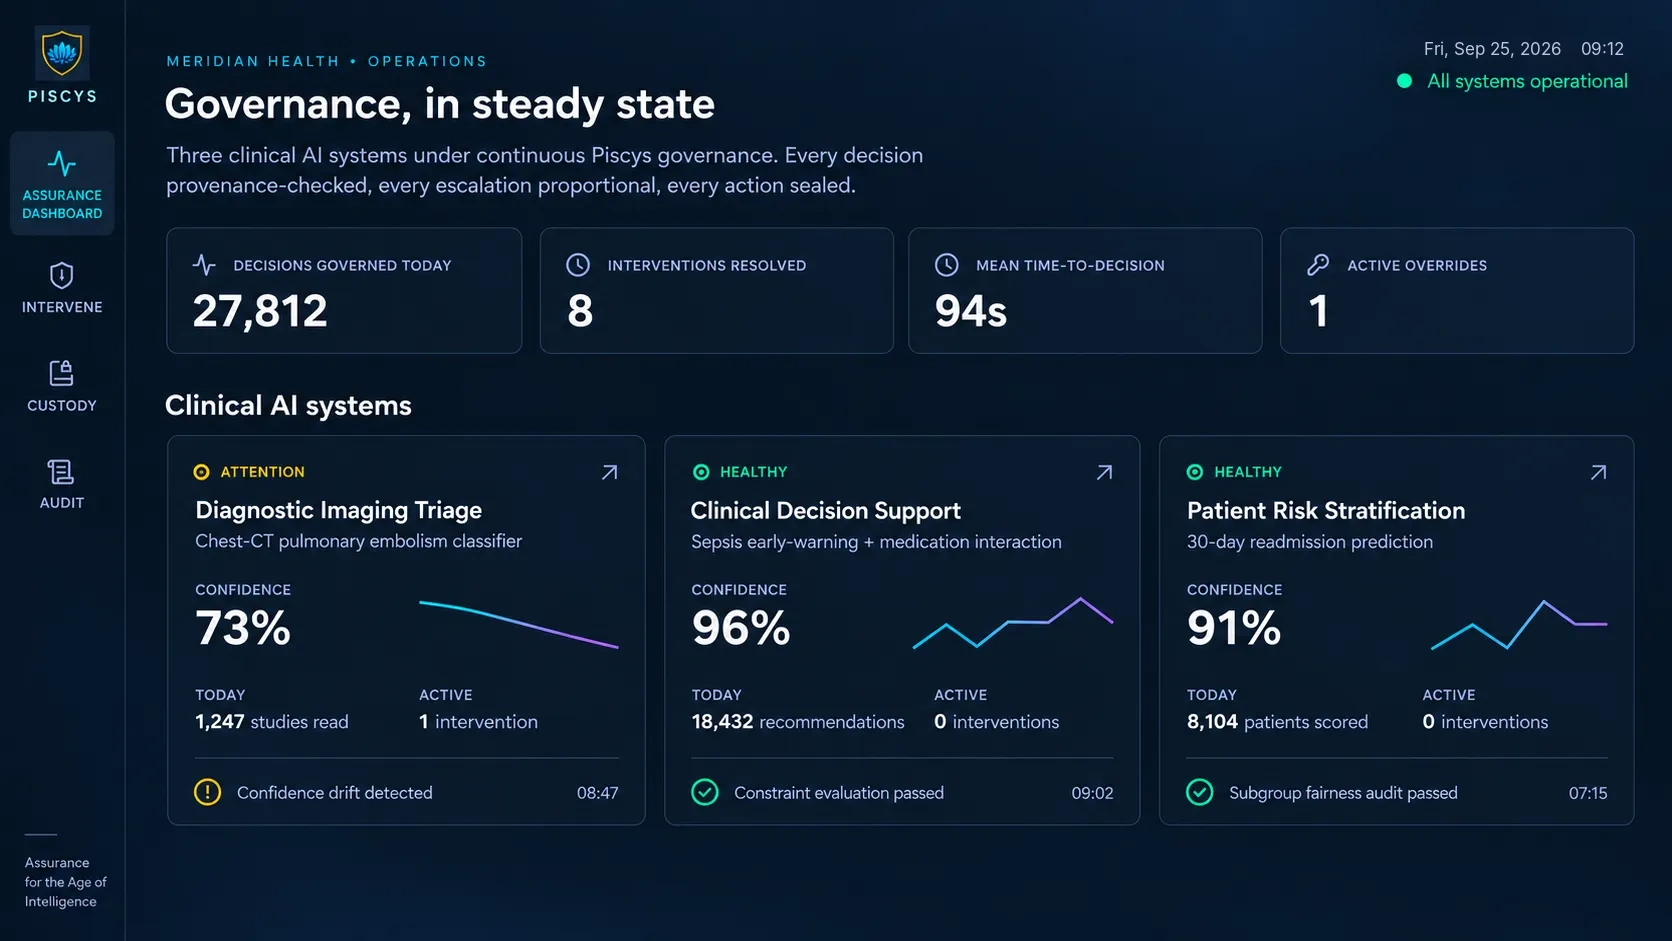
01 / Assurance Dashboard
See What Requires Attention
An illustrative oversight view of operational signals, material risk conditions, interventions, and supporting evidence.
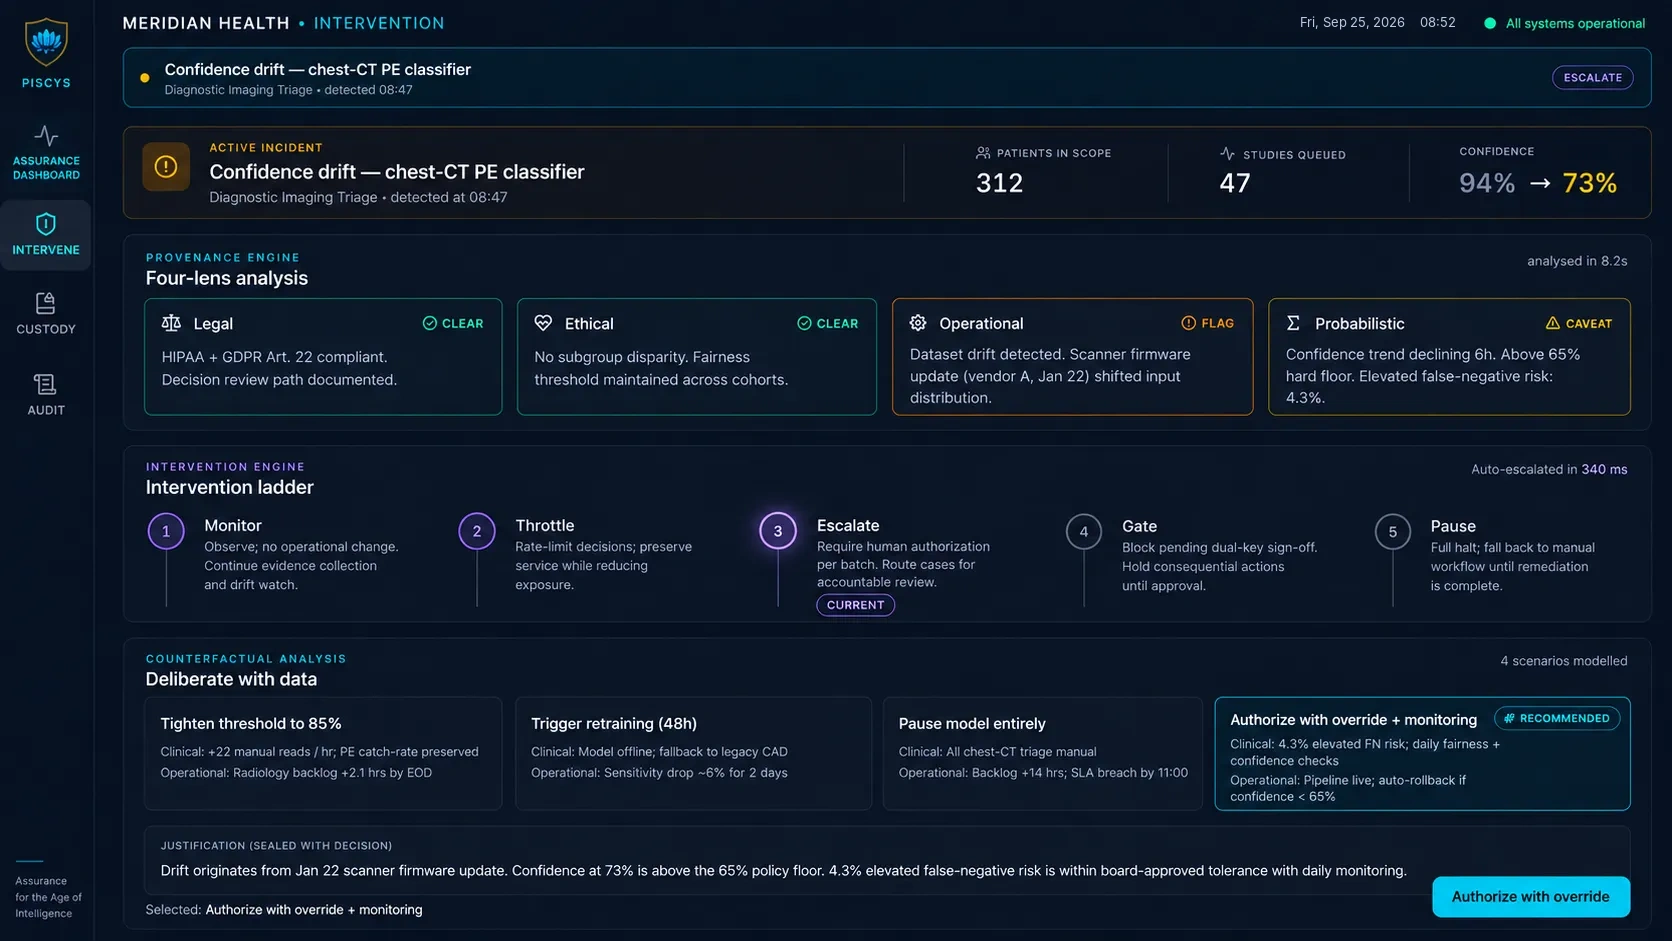
02 / Evaluate & Intervene
Apply Proportionate Safeguards
Explore how a consequential AI action could be evaluated against configured constraints and routed toward an appropriate response.
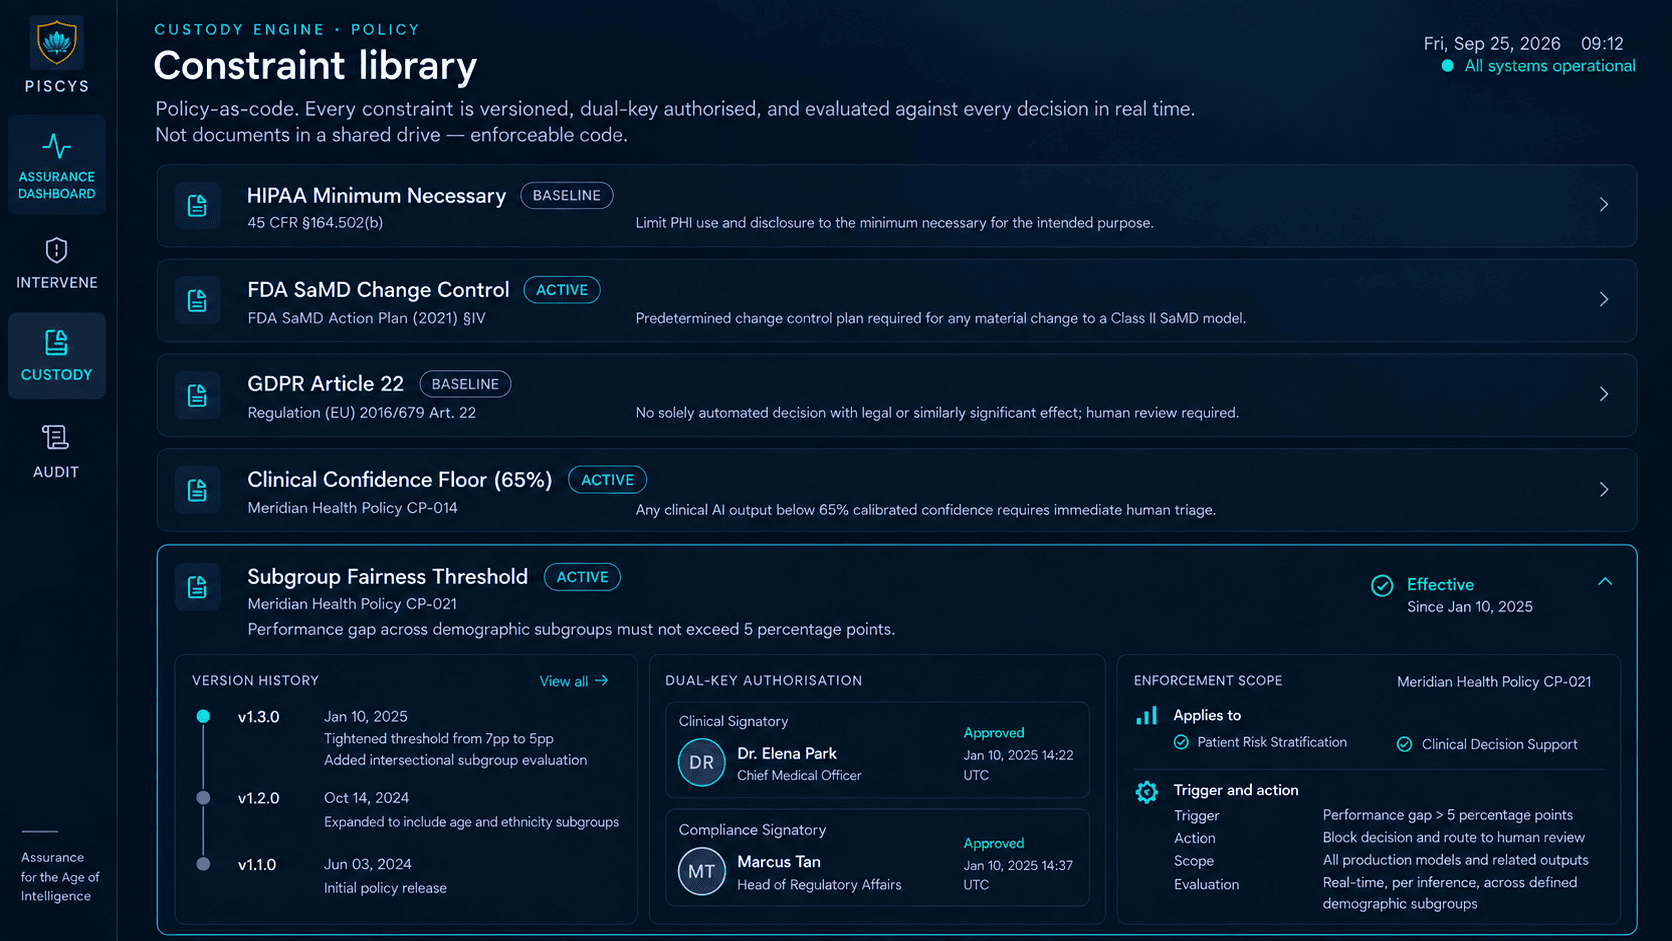
03 / Govern Authority
Keep Decision Rights Accountable
See how significant actions, approvals, and exceptions could involve explicitly authorized human decision-makers.
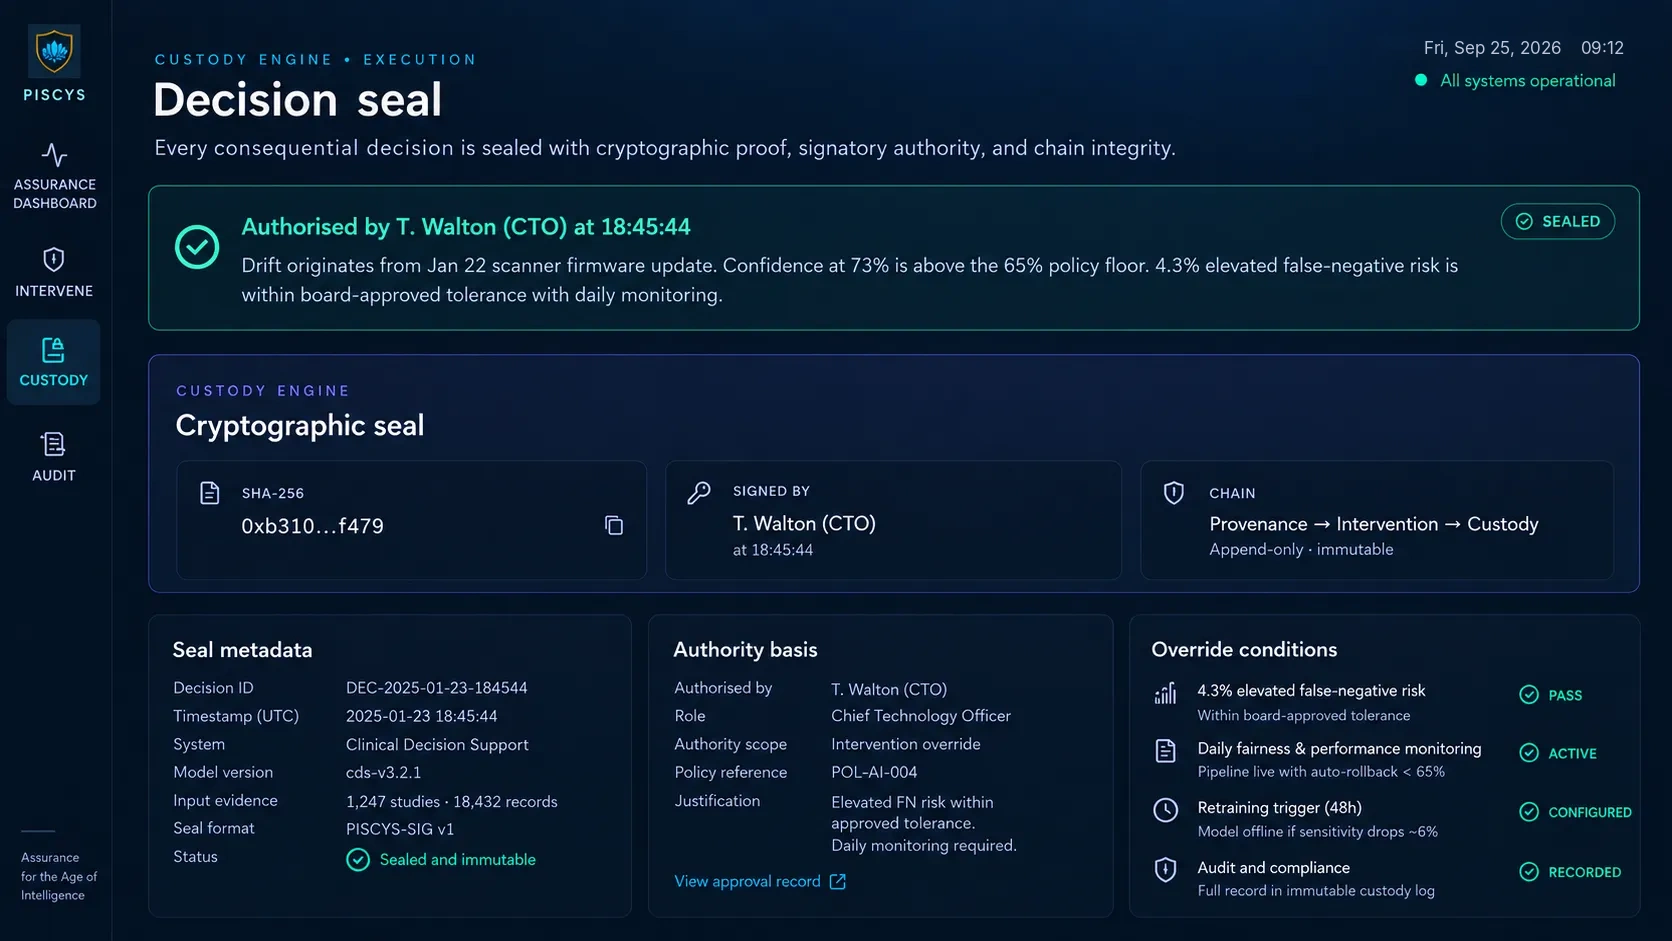
04 / Seal Decisions
Preserve the Decision Record
Explore the proposed experience for documenting authorized decisions, their context, and the evidence needed for subsequent verification.
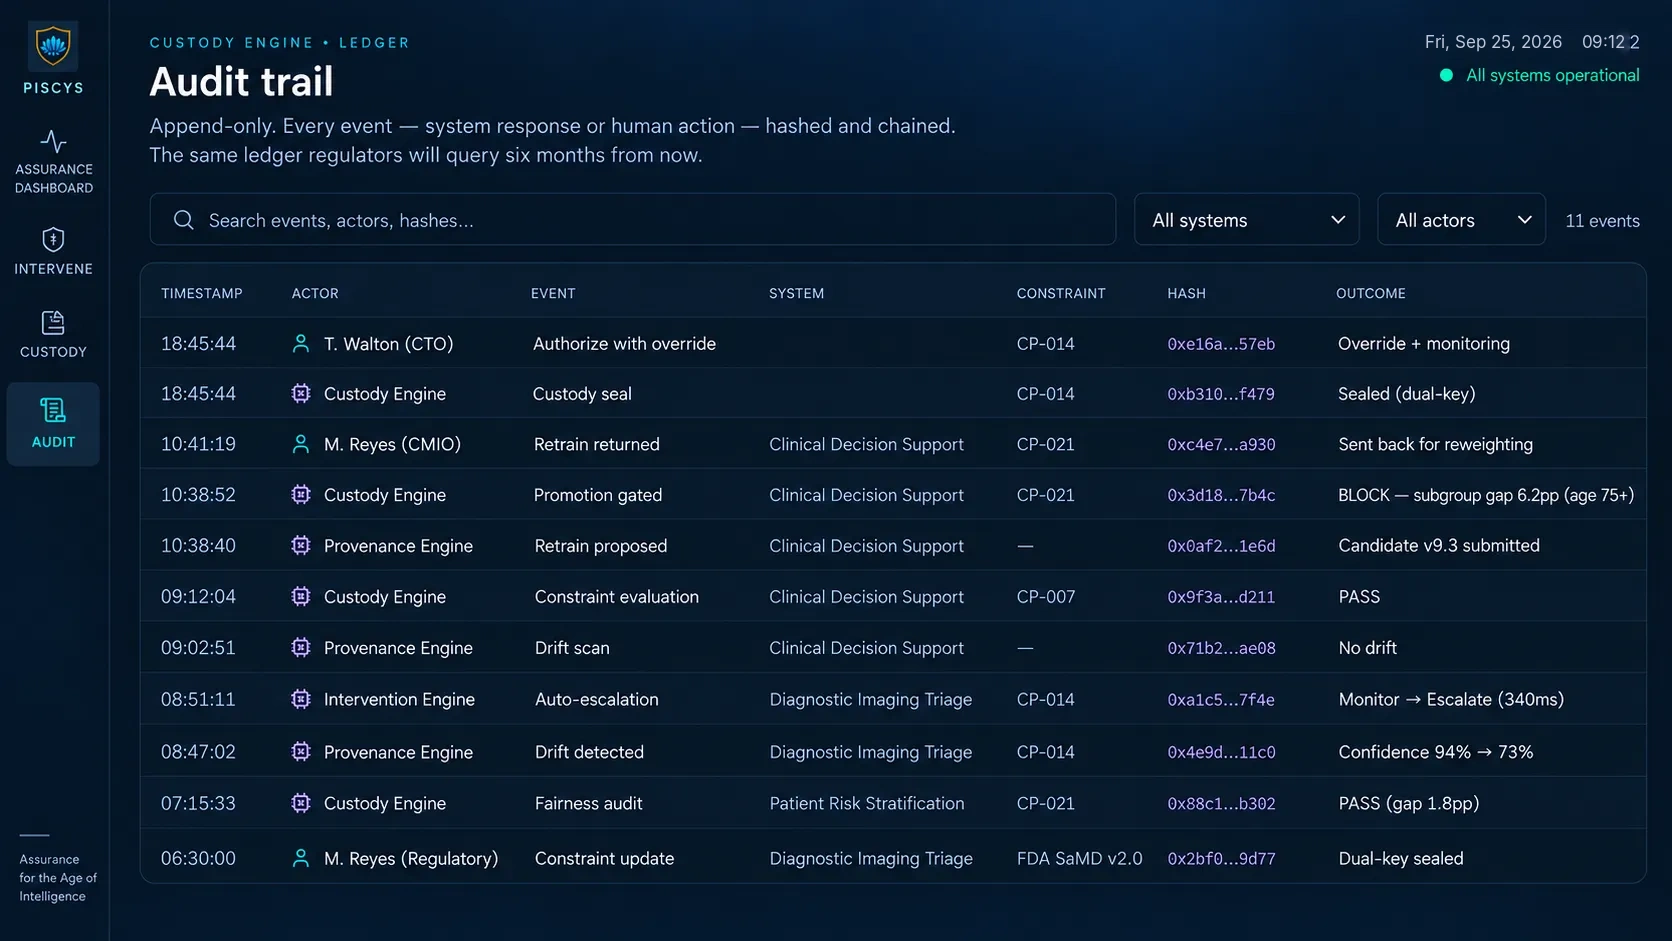
05 / Audit Evidence
Make Governance Reviewable
See how an oversight team could examine recorded actions, applicable controls, interventions, and supporting evidence.
Explore the Full Concept in Figma →
These screens illustrate proposed user experiences, not a mandatory processing sequence or validated production capabilities. Actual implementation and integration boundaries remain in development.
09 / Engage Piscys
Start With the Workflow Where Control Matters Most
Founder-led advisory engagements help enterprise teams clarify accountability, identify control gaps, and translate governance requirements into practical design priorities.
Start with a focused executive conversation. Expand into assessment or implementation design where warranted.
01 / Align
Executive Briefing
Examine a consequential AI workflow, its governance challenges, and practical next steps.
Executive alignment and scoped next-step options
02 / Assess
Readiness Assessment
Review control gaps, decision authority, evidence maturity, and escalation requirements.
Prioritized findings and assessment recommendations
03 / Design
Implementation Design Sprint
Translate agreed requirements into proposed controls, intervention playbooks, and evidence specifications.
Workflow-specific design artifacts
Let's Discuss Your Highest-Consequence
AI Workflow
Advisory services available now. Platform capabilities remain in development.
Start a Conversation
Explore your organization’s AI governance priorities and identify practical next steps.
Share The Platform
Explore a lighthouse design partnership to help define priority workflows, control requirements, and future platform validation.